Data flow diagram
What data Cliqer moves, over which channels, how it is encrypted and where it is stored.
This page describes every data flow in Cliqer, the protocol and encryption used on each, and what is stored versus what stays transient. It is written for security and procurement reviews. For the component-level view, see the Solution blueprint. For firewall rules and ports, see Security & Networking.
Diagram
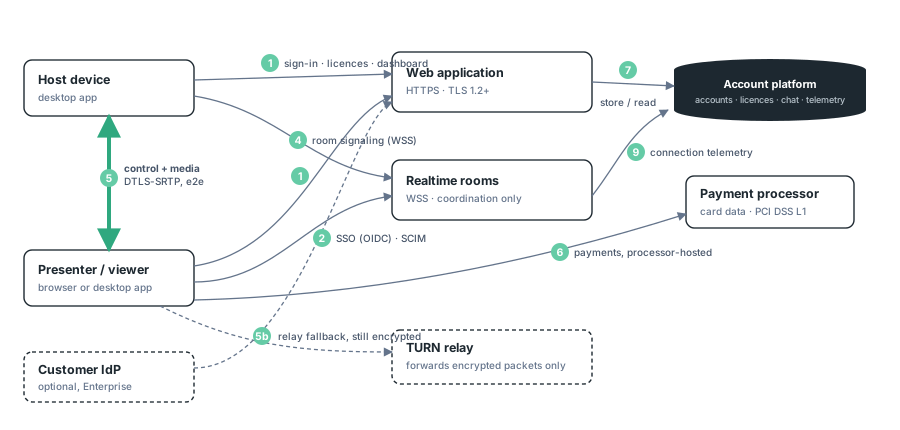
Flows
| # | Flow | Channel | Encryption in transit | Data carried | Stored? |
|---|---|---|---|---|---|
| 1 | Sign-in and dashboard | HTTPS (TLS 1.2+) | TLS | Credentials or passkey assertion, profile (name, email), team, licence and subscription records | Yes - account platform |
| 2 | SSO (optional) | HTTPS, OIDC authorisation code flow | TLS | Identity claims from your IdP (email, name). With "Require SSO" enabled, no passwords are handled by Cliqer | Identity link only |
| 3 | SCIM (optional) | HTTPS, bearer token minted by your team | TLS | Member create / update / deactivate events from your IdP | Yes - team membership |
| 4 | Room signalling | WSS (TLS 1.2+) | TLS | Room ID, display names, peer IDs, presence, connection metadata. No presentation content | Transient coordination state |
| 5 | Session control and media | WebRTC, direct peer to peer | DTLS 1.2, SRTP | Slide commands, pointer position, timer state, camera / screen streams | No - never stored. Goes directly between participants when a direct connection can be made |
| 5b | Relay fallback | WebRTC via TURN (UDP/TCP/TLS) | DTLS 1.2, SRTP | Same as flow 5. The relay forwards encrypted packets and cannot decrypt them | No |
| 5c | Server relay fallback | WSS through the application servers | TLS | Same as flow 5: control commands, chat and screen frames, forwarded by our servers only when neither a direct nor a relayed WebRTC connection can be made | No - forwarded, never stored |
| 6 | Payments | HTTPS to processor-hosted pages | TLS | Card data goes to the payment processor only (PCI DSS Level 1). Cliqer stores subscription and invoice metadata, never card numbers | Metadata only |
| 7 | Support chat (website messenger, optional) | HTTPS + WSS | TLS | Support conversations with Cliqer: messages and image attachments. Separate from sessions; in-session chat is text-only, peer to peer, never stored | Yes - account platform |
| 8 | Transactional email | SMTP / HTTPS from platform | TLS | Receipts, team invites, security notifications | Send log only |
| 9 | Operational telemetry | HTTPS | TLS | Connection events (timestamps, room ID, connect / disconnect outcome) used for service reliability. No session content | Yes - operations store |
Key properties
- Presentation content stays on your devices. Slides are never uploaded to Cliqer. What travels between participants is control commands and, when you enable them, camera or screen streams - always encrypted in transit.
- Media and control are encrypted in transit. Between participants they normally travel directly over WebRTC, protected by DTLS-SRTP. On locked-down networks the TURN relay forwards the encrypted packets without the keys to decrypt them. When neither works, our application servers relay the data over TLS-protected WebSocket connections and do not store it.
- Signalling carries coordination metadata only - who is in the room and how to reach them, not what is being presented.
- No card data on Cliqer systems. Checkout and the billing portal are hosted by our payment processor.
- All server communication is TLS. There is no unencrypted listener; HTTP redirects to HTTPS, and WebSocket connections are WSS only.
Storage and third parties
| Store / party | Role | Data |
|---|---|---|
| Cliqer account platform | System of record | Accounts, teams, licences, subscriptions, support conversations |
| Cliqer application platform | Cliqer-operated dedicated infrastructure: web application, realtime coordination, storage | Coordination state, uploaded assets, operational telemetry |
| Edge network provider | Traffic transit, TLS termination, DDoS protection, STUN/TURN relay; until the standby copy is retired (about 2026-10-24), storage of that copy for rollback | Traffic in transit; until then, a standby copy of connection history (including IP addresses and display names), device-account and device-trial records (device IDs, IP addresses), and session coordination state |
| Payment processor | PCI DSS Level 1 | Card and payment data |
| Your identity provider (optional) | SSO and SCIM source | Identity claims, membership lifecycle |
Questions from a vendor security review we have not answered here - use the contact form and we will respond directly, including the named subprocessor list under NDA.